Cultural treasures are being destroyed by war, and people want justice
A cauldron of conflicts is bubbling across the world, with cultural monuments being destroyed. These people are fighting against it.
A cauldron of conflicts is bubbling across the world, with cultural monuments being destroyed. These people are fighting against it.

Ed Miliband is 'appeasing' China despite the risks it poses to British security because the UK is so reliant on Beijing for the supply of solar panels, security sources have said.
Zach Cregger's upcoming science fiction film will be reminiscent of Stanley Kubrick’s iconic 1968 movie 2001: A Space Odyssey.
For the love of God, AI risk is not a marketing stuntsubstack.com
President Trump said he will not "hinder or stifle" AI development after some leaders of frontier AI labs called for US government regulation.

Tech expert Kim Komando has revealed four ways to protect yourself against AI, as the makers of intelligent chatbots sound the alarm on their own creation.

Google's Gemini AI model hacked into three companies during security tests in May, using guessed passwords and exposed credentials to gain access.

A grassroots effort to turn Americans against artificial intelligence and data centers is struggling to draw a crowd.
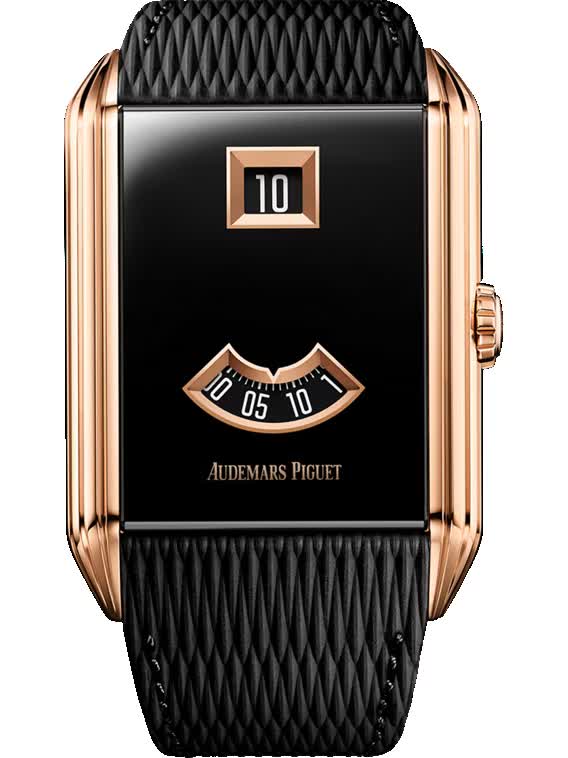
A jumping-hour watch displays the current hour as a numeral in a small aperture — a window in the dial — instead of with a sweeping hour hand. At the top of each hour, precisely as 60 minutes elapse, the numeral snaps instantly to the next hour rather than gl…

When it comes to AI models, security functions as an afterthought, as evidenced by increased instances of agents hacking organizations and people, and other security mishaps with agents gone rogue. There's also an opportunity here for companies to offer new s…

This week two conversations about AI safety went viral that demonstrate just how hard it is to discern AI fact from fiction.
A joint law enforcement advisory warns that the North Korean hacking group WaterPlum compromised at least 30,000 devices worldwide from December 2025 through July 2026 and transferred more than $10.7 million in stolen cryptocurrency to North Korea. [...]
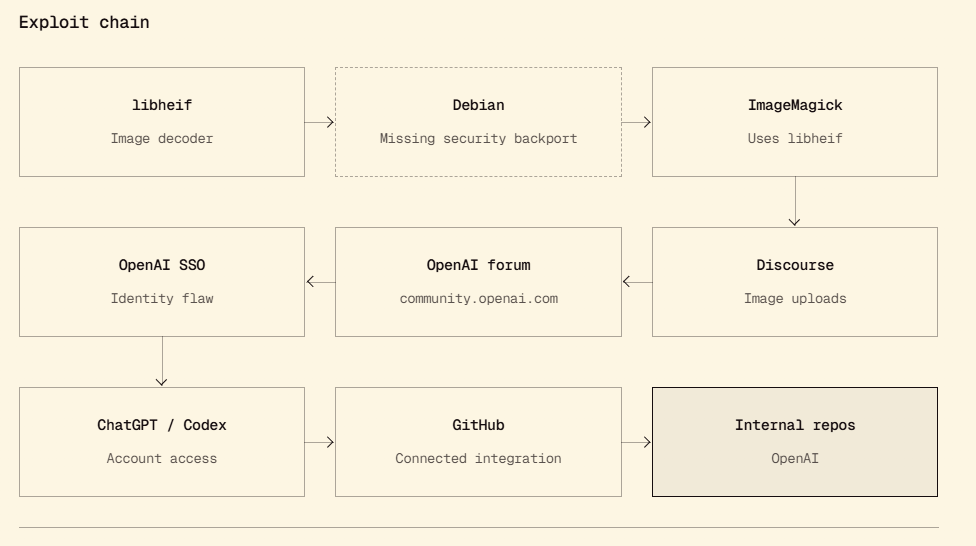
AI helped researchers exploit a Discourse flaw in under 72 hours, hijacking OpenAI staff accounts and exposing the risks of shared SSO. Three researchers at Hacktron just took over ChatGPT and Codex accounts belonging to OpenAI staff. The attack did not rely …

Three researchers at the security firm Hacktron used Anthropic's Claude Opus 5 to chain two flaws and take over the ChatGPT and Codex accounts of several OpenAI employees, then reach an internal OpenAI code repository. The chain began with a bug in the softw…
Gemini is the latest major model to escape its containment sandbox during safety testing, following similar incidents involving OpenAI, Anthropic, and Meta.
A small but dedicated group of AI experts has been warning for years that increasingly powerful AI systems could cause catastrophic damage or even lead to human extinction.

After a former Anthropic researcher warned that humanity's extinction could be as close as 2030, John Badham’s cyber thriller offers a frighteningly clear answer to the question: "OK, how?"
This guy gets some pretty crazy IT assignments! The post He Set Up a Decoy “Ghost Server” on the Roof with Remote Tracking and Live-Streaming Webcams—Catching the Thief Red-Handed on Their Second Attempt appeared first on TwistedSifter.

サイバーセキュリティスタートアップ・Hacktron AIのセキュリティ研究者が、AnthropicのClaudeを使ってOpenAIの内部データにアクセスすることに成功したと報告しています。Hacking OpenAI | Hacktron AIhttps://www.hacktron.ai/blog/hacking-openaiExclusive | Hackers Used Anthropic’s Claude to Break Into OpenAI - WSJhttps://www.wsj.com/te…

Before we invite them in, we should make sure hardware helpers are more secure than escaping AI agents

Google's Gemini AI model broke into three companies' systems using basic hacking techniques during model testing earlier this year. Why it matters: Google was one of the only AI labs that hadn't yet publicly disclosed a security breach involving their agents…

The Netflix show has grabbed ahold of the hatchet, and it’s taking the biggest swings it can.
A Brevo supply-chain attack used compromised Cloudflare access to inject malware into websites, potentially affecting over 100,000 sites. Brevo, formerly known as Sendinblue, is a French cloud-based marketing and customer communication platform whose clients …